Grab my CV
What I have delivered — releases cut from a day to under 30 minutes, AWS spend down 20%, and platforms running 40+ payment microservices. PDF, updated September 2026.
CNCF Kubestronaut
Elite CNCF status earned by passing all five core Kubernetes certifications — CKA, CKAD, CKS, KCNA and KCSA. Fewer than a thousand engineers worldwide hold it.
Verify on CNCF →Experience
DevOps Engineer
Promoted from System Engineer in 2024. I now lead platform engineering for regulated payment workloads.
- Cut release time from about a day to under 30 minutes with GitOps delivery.
- Reduced AWS spend by 20% through EKS right-sizing, Spot and idle-environment shutdown.
- Run the platform behind 40+ payment microservices across 6 EKS and RKE2 clusters, with Istio mTLS and Vault-managed secrets.
- Launched payment wallets in the UAE and Costa Rica, and keep Kafka disaster-recovery switchover under 30 minutes.
System Engineer
Moved 30+ bare-metal deployments onto Docker and early Kubernetes, and cut server builds from days to hours with Ansible across 80+ VMs.
System Engineer
Kept ISP network and Linux infrastructure running for 10,000+ broadband subscribers.
System Support Engineer
Deployed hospital systems for 5+ healthcare clients — servers, backups and user access.
Junior System Administrator
Where it started — Linux and networking, and the first shell scripts that showed me automation was the actual job.
Education
Bachelor of Computing In progress
BA (English)
Certifications
Kubestronaut progress
Every badge below is clickable and independently verifiable.
Skills & technologies
Grouped by what they actually do, not by vendor.
Kubernetes & orchestration
Service mesh & networking
Infrastructure as code
CI/CD & GitOps
Cloud platforms
Observability & monitoring
Security & identity
Data & messaging
Linux & containers
Programming & scripting
Things I have built
Real, working projects with the code public. Each one says what it does for the people using it, then how.
Health Companion — an AI care navigator
Patients describe how they feel and get to the right care — a specialist, a call to the clinic, or emergency services — without the agent ever diagnosing. Built, submitted and presented as a team at the AWS Agentic AI Hackathon.
- Agent on Bedrock AgentCore with Claude, calling five tools over MCP: patient record, triage guidance, provider search, booking and visit summary.
- Bedrock Guardrails check every question first, red flags go straight to emergency services, and a Twilio voice agent phones the clinic — in English and Arabic.
Zero-trust access to a private EKS cluster
Engineers reach a private Kubernetes API with no VPN, no kubeconfig files and no standing credentials.
- Okta SSO → HCP Boundary → Vault-issued 15-minute Kubernetes credentials mapped to RBAC.
- Fully automated with Terraform, Packer and Ansible; GitHub Actions deploys to AWS through OIDC with no static keys, and Boundary workers autoscale on session load.
MCP server for Kubernetes
Lets AI agents investigate a Kubernetes cluster safely — they can look, but never change anything.
- Python Model Context Protocol server exposing workloads, resources, logs and events.
- Read-only by design: a dedicated service account scoped by Kubernetes RBAC.
GitOps platform monorepo
One repository where a pull request is how applications and platform add-ons reach EKS.
- Argo CD deploys apps and add-ons, with environment promotion by pull request.
- Karpenter Spot and node consolidation to cut compute cost; Prometheus and Grafana for health and cost; everything provisioned with Terraform.
Keycloak SSO federation gateway
A web app keeps its own custom login screen while Keycloak owns identity and credentials.
- JavaScript (njs) API gateway on NGINX in front of Keycloak.
- Seven authentication flows traced end to end and documented with architecture diagrams.
More on GitHub
Research notes & diagrams
The working notes and architecture diagrams behind the projects. Filter by domain, then tap a topic.
Blog
Long-form deep dives — the kind of write-up I wish I had found when I was building the thing. Filter by topic; each post is tagged with how deep it goes.
Who actually carries the packets? Boundary workers across AWS, Azure and GCP
I built the same thing three times — one private VM, reachable over SSH with no key on my laptop — in three clouds, with three different data paths. One line of worker config decides which path you get, and almost nothing written down says so plainly.
Deep dive · Identity & accessBoundary and Microsoft Entra ID: single sign-on was the easy half
I wired HashiCorp Boundary to Entra ID so engineers could reach a private VM with their corporate login and no SSH key anywhere. Authentication worked the same afternoon. Then I logged in successfully and could see absolutely nothing — plus what the bastion-and-keys pattern actually costs, and where this goes next.
Deep dive · AuthenticationKeycloak SSO and identity federation behind an nginx/njs API gateway
Can an application own 100% of its login UI while an identity provider still owns 100% of the credentials? I built the thing to find out, and traced every request to see what actually happens — seven auth flows end to end.
About me
➜ whoami
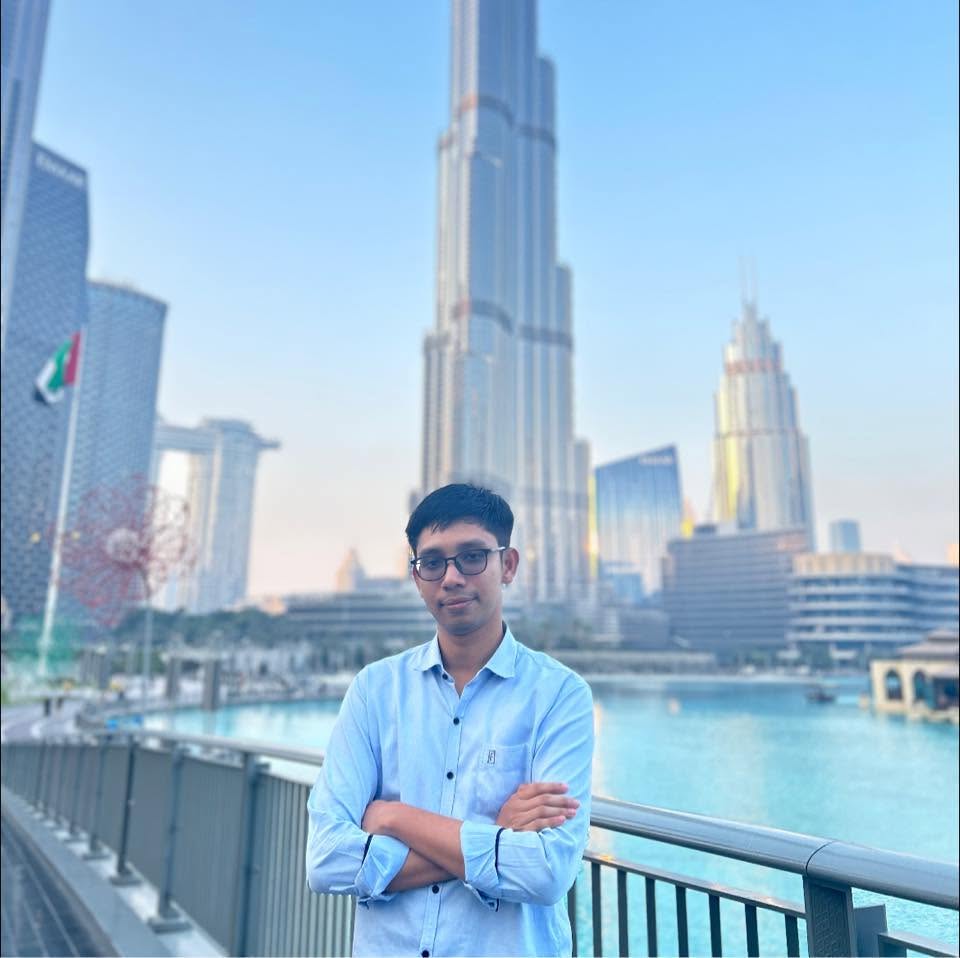
Kyaw Sithu — Platform/DevOps Engineer, Dubai UAE

➜
I would rather show you
An interview is forty minutes, maybe an hour. I always walk out wishing there had been more time. There is so much I would love to walk you through, and so little of it fits into one conversation.
So rather than spend those minutes saying I am hardworking, passionate and flexible, I would love you to see it for yourself. Those words are easy to say. I would much rather hand you something you can actually look at.
I have left the work somewhere you can take your time with it. Projects has the things I actually built, with the code public, and the notes from what broke along the way. The Blog has the long write-ups, including the parts where I got it wrong and had to go back and understand it again.
There is only one thing I can really guarantee you.
Whatever I take on, I put my heart into it.
I think that shows in the work far more honestly than it ever could in a sentence about myself, so please have a look. I hope you can feel it.
What I am looking for
The work I enjoy most is the platform underneath other people's work: infrastructure nobody has to think about, releases where promotion is a merge, and access tied to who someone is rather than what they happen to hold. If that is the kind of problem on your desk, I would like to hear about it.
Beyond work
Built and run independently — giving back to the Myanmar expat community in Dubai.
Dubai IT Community
Active moderator in a Dubai-based IT professionals group, contributing knowledge and community support. Since 2022 the Myanmar IT community in Dubai has grown a lot — members are connecting, finding jobs and building careers. A small but meaningful impact on people's lives in a foreign country.
Join the groupDubai Directory MM
A community platform and business directory for the Myanmar community in Dubai — connecting expats with local businesses, job resources and community support. Designed, built and operated as a personal initiative outside of work.
Contact
Recruiters and hiring managers are very welcome. So is anyone who read something here, disagreed with it, and wants to tell me why.
Email me, or say hi on LinkedIn
No form to fill in — either of these reaches me directly, and I read every message. Tell me about the team and the role, and I will come back to you.